AI Security & Governance
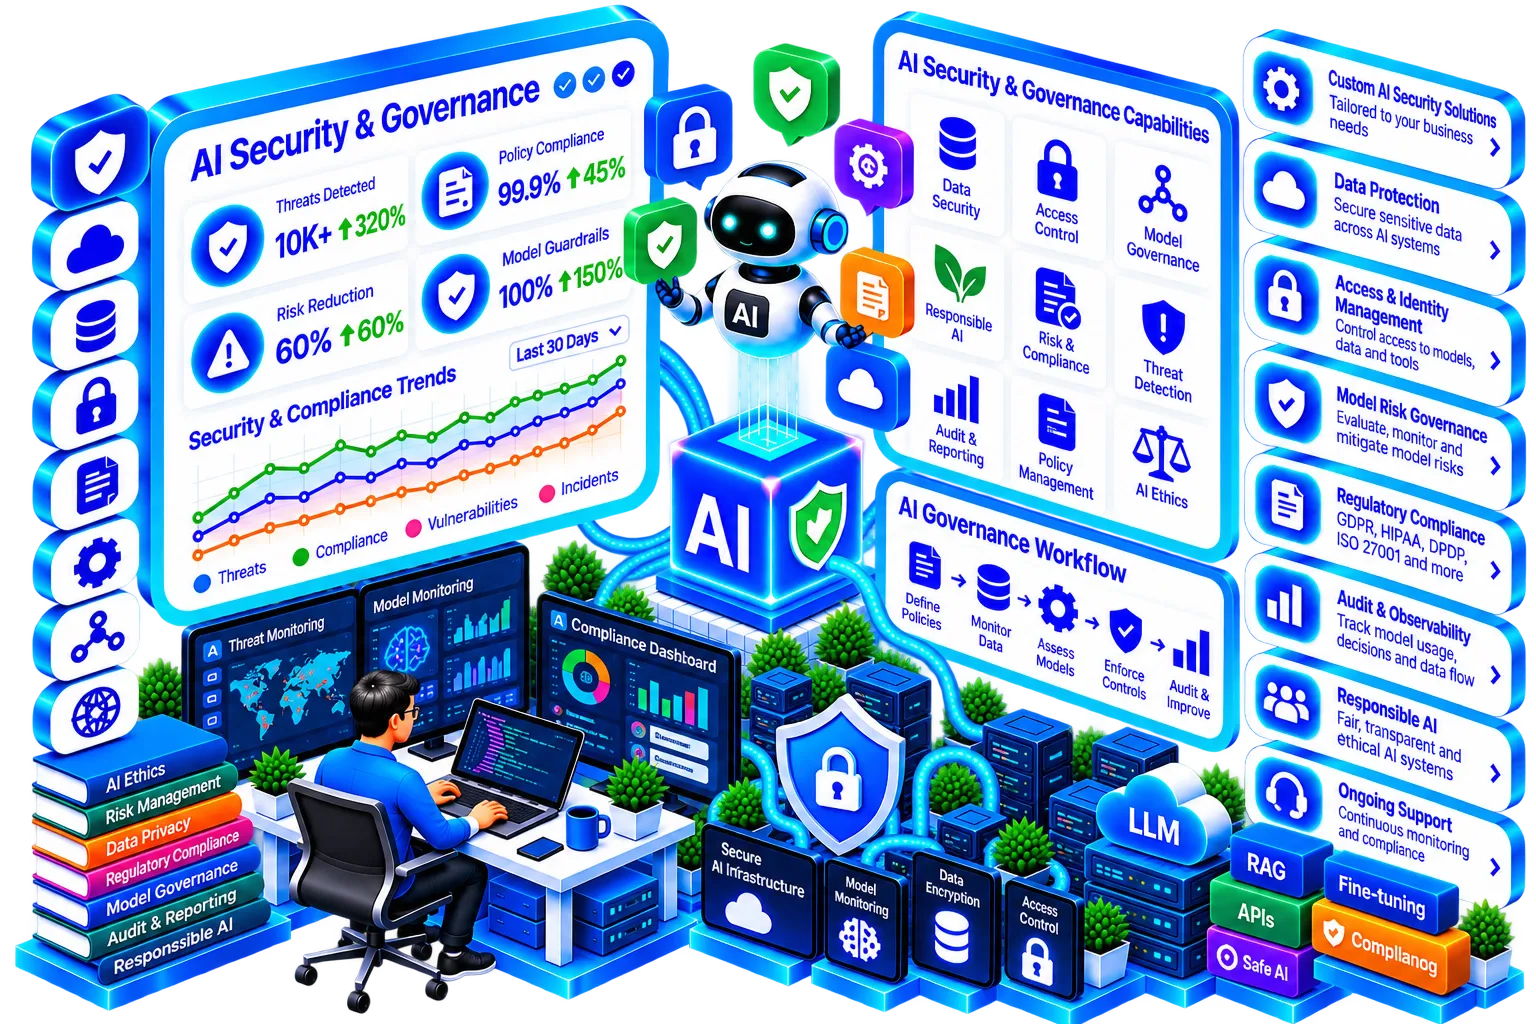
Why AI Security & Governance
- An inventory of AI systems, data access and decision boundaries
- Risk and compliance findings mapped to your actual use case
- Human-review rules for high-impact or uncertain outputs
- Access controls, audit trails and documented ownership
- A practical governance plan your security, product and compliance teams can use
As AI systems touch more sensitive decisions, the questions get harder: what data was used, who can access what, what happens when the model is wrong.
DashCloud's AI security and governance work builds these controls in from the start — access boundaries, audit trails, risk review — so an AI system holds up under scrutiny, not just under normal use.
Inside AI Security & Governance
Responsible AI practices
Building AI systems with clear boundaries on what they can decide autonomously versus what requires human review.
- →Boundaries for autonomous actions
- →Human review for high-stakes decisions
- →Clear escalation when the system is uncertain
OUTPUT Responsible AI controls and review flow
AI risk and compliance
Risk assessment and compliance controls scoped to your industry's regulatory requirements, built into the system rather than added after.
- →AI risk and regulatory requirements review
- →Evidence and documentation for audit
- →Controls built into the delivery process
OUTPUT Risk register and compliance-ready documentation
Deepfake and content authenticity detection
Detecting AI-generated or manipulated content, for organizations that need to verify authenticity at scale.
- →Signals for manipulated or generated content
- →Review workflow for disputed authenticity
- →Detection scoped to your content and threat model
OUTPUT Content authenticity detection workflow
Make AI safe to operate
Regulated industry teams
Deploy AI systems that hold up to audit and compliance review.
Security teams
Understand and control what an AI system can access and act on.
Trust and safety teams
Detect AI-generated or manipulated content at scale.
People and HR teams
Add human review and clear decision boundaries to sensitive workflows.
Finance and risk teams
Make AI decisions traceable, explainable and governed inside financial processes.
Legal and compliance leaders
Turn policy requirements into practical controls that teams can operate.
Built around real teams
Regulated industry teams
Deploy AI systems that hold up to audit and compliance review.
- Which AI decisions need a person involved?
- What can the system do on its own?
- How do we handle an uncertain result?
Security teams
Understand and control what an AI system can access and act on.
- What data can the model access?
- Which actions need stronger permissions?
- What evidence would an auditor need?
Trust & safety teams
Detect AI-generated or manipulated content at scale.
- How do we verify content is authentic?
- What happens when detection is inconclusive?
- Who reviews a disputed result?
From AI risk review to controls you can defend
- 01
Map
Identify the AI systems, data, users and decisions in scope, including where access and autonomy create risk.
Output: AI system and risk scope - 02
Assess
Review failure modes, regulatory obligations and the controls needed for your industry and use case.
Output: Risk assessment and control plan - 03
Implement
Build access boundaries, audit trails, review steps and content checks into the system.
Output: Implemented controls and audit trail - 04
Govern
Document ownership and review processes so controls remain useful as models, data and requirements change.
Output: Governance ownership and review process
Review one system, or build a governance layer
AI risk review
Understand the risks and control gaps in one existing or planned AI system.
- ✓System and data inventory
- ✓Risk and compliance assessment
- ✓Control recommendations
- ✓Prioritized remediation plan
Governance foundation
Build responsible AI, security and audit controls into the systems your teams operate.
- ✓Risk and policy framework
- ✓Access and decision boundaries
- ✓Human review and audit trails
- ✓Operating documentation and ownership
Governance support
Keep controls aligned as your models, data, regulations and use cases change.
- ✓Regular risk reviews
- ✓New model or feature assessments
- ✓Audit and compliance support
- ✓Updates to controls and guidance
Everything you need to know
Still have questions?
Can't find what you're looking for? Talk to our team and we'll point you in the right direction.
Contact usWe scope compliance requirements to your specific industry and regulatory context during the engagement — this varies enough that it's worth a direct conversation.
Concretely: defined boundaries on autonomous action, audit trails on decisions, and human review built in for anything high-stakes — see also AI Agents Development for how this plays out for autonomous systems.
Yes — governance and security review can be layered onto an existing AI system, not just a new build.